


NOTABLE ACCOMPLISHMENTS & PROJECTS
from
2025
TO
Present
(1+ Year)Critical Infrastructure
eID AI Security Scan: Agentic AI for the EUDI Wallet
Bridging Offensive AI and Government-Grade Secrecy: To secure Android-based eID implementations and the European EUDI Wallet reference architecture, I engineered a fully automated, agentic AI pentesting scanner from scratch. This system eliminates the friction between rigid public sector compliance and cutting-edge offensive AI capabilities.
Hybrid Methodology & Technical Execution: The system merges deep Static Application Security Testing (SAST) with dynamic runtime analysis (DAST) via Frida. It autonomously performs AI threat modeling (TARA-AI aligned), evaluates hardware-backed cryptographic operations (Secure Enclave, Keystore), complex authentication flows (OIDC4VP, SIOPv2), and certificate pinning bypasses, concluding with fully actionable Proof of Concept (PoC) validation.
NDA Compliance & Privacy-by-Design (Public Sector Foundation): Cloud-based AI traditionally hits a hard wall in government environments due to data privacy concerns. My architecture solves this at its core: Operating as a strict Data Sovereignty Engine, all sensitive eID infrastructure data and backend communications remain entirely local. External LLM APIs are strictly flag-gated, subjected to automated secret redaction, and utilized exclusively for sanitized, atomic decision trees. Architectural data leakage is impossible.
Government-Compliant Audit Mapping: Every identified attack vector is deterministically mapped against the eIDAS 2.0 Architecture and Reference Framework (ARF), BSI TR-03124 (eID-Client), BSI TR-03110, and ISO/IEC 18013-5 (Proximity/mDL). The output provides tangible, immediately auditable reports tailored for both technical decision-makers and project managers.
from
2023
TO
Present
(3+ Years)Agentic AI Development
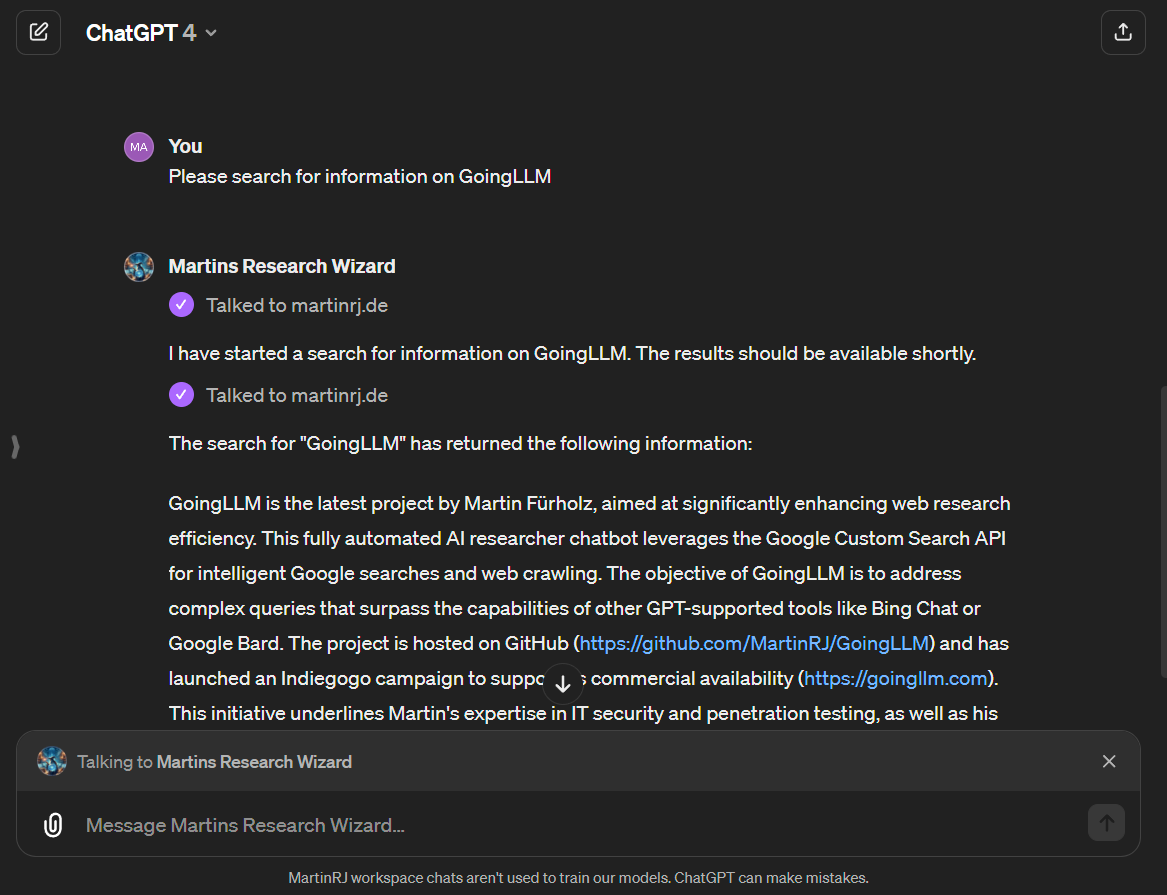
GoingLLM: The Autonomous Intelligence Backbone
Visionary Timing: I architected in Python and deployed GoingLLM in early 2023, ahead of mainstream agentic AI. Recognizing the limitations of static models early on, I built an autonomous agent capable of intelligent live reconnaissance, OSINT, and complex vulnerability correlation.
100% Autonomous Dark Web & OpSec Architecture: While basic web search is now a commodity, GoingLLM remains my proprietary engine for deep-dive threat intelligence. Since 2024, a specialized Dark Web analysis variant built for a major global film and entertainment studio has operated 100% autonomously via AI for operational security (eliminating manual Dark Web browsing altogether).
Enterprise Impact: This autonomous pipeline delivers critical intelligence reports on piracy and DRM circumvention trends directly for enterprise security stakeholders, answering investigative questions that commercial AI tools cannot handle and serving as the blueprint for subsequent autonomous DRM-security and AI Red-Teaming engagements.
Today, GoingLLM acts as the neural backbone for my suite of custom agentic testing tools, continuously updated to leverage GPT-6, custom Search APIs, and advanced crawling logic.
Visit Project Website: goingllm.com
from
2016
TO
05/2026
(10 Years)Security SME & TTL
Global Security Operations, Triage & AI Red-Teaming
Exclusive Test Team Lead & Security SME (11/2018-05/2026; Security Practice since 03/2016): Across roughly five penetration tests per week at the world's largest crowdtesting provider, I served as the technical lead, gatekeeper, and escalation specialist for teams of up to 30 pentesters across hundreds of products, ranging from small online shops to global tech leaders, financial institutions, major film studios, telecommunications providers, and international publishers. I designed the practice's smoke-testing, bug triage, and fix-verification workflows, advised leadership on project effort scoping, and personally reproduced, triaged, and manually fix-verified roughly 10,000 vulnerability reports (every report passing through my hands twice, including direct developer ticket and technical escalation communications).
Hands-On Escalation Specialist, Full-Spectrum Pentesting & DRM Forensics: Alongside leading triage, I remained one of the practice's most active hands-on pentesters across Web and REST/SOAP APIs (OWASP Top 10, OAuth 2.0/OIDC, SAML, JWT) as well as Mobile (Android/iOS via Frida and MobSF), and served as the go-to specialist for single-VPN and high-complexity scopes. Key assignments included multi-week manual white-box security code reviews and accompanying internal/AWS subnet pentests for a financial-sector client (identifying 28 vulnerabilities in a single subnet in December 2025), OSCP-scope host and Active Directory assessments, IoT hardware, Windows/macOS/UWP desktop suites and browser extensions, Web/Mobile/Desktop DRM circumvention testing, custom-automated Fiddler-log DRM compliance forensics for streaming providers, and security audits of LLM-integrated MCP tools.
Core Tooling & Engineering Stack: Daily mastery of Burp Suite, Frida, MobSF, Nmap, Wireshark, sqlmap, ffuf, and Postman, backed by custom exploit, triage, and autonomous AI tool development in Python, C#, C++, Java, SQL, Bash, PowerShell, and Docker.
AI Red-Teaming Foundation & Academy Curricula (2021-2026): Starting in 2024, I co-planned AI security engagements with project management and developed the initial end-to-end LLM testing blueprints, effort estimates, client pitch decks, and test suites (from an enterprise HR AI chatbot to unreleased frontier models from leading AI labs). I hand-wrote a comprehensive 60+ page internal "AI Red-Teaming Field Guide" aligned with MITRE ATLAS, NIST AI RMF, and OWASP LLM Top 10, trained both management and testers on how to execute AI Red-Teaming, and built custom agentic automation for complex engagements. Earlier, I authored the official Academy courses for API Testing and Security Testing (backed by a custom REST/Postman API sandbox) and delivered three two-day Web Application Security Training sessions in Manhattan/NYC (10/2018) for 70 IT and development staff of a major international publisher.
Verified Track Record (1,544 Approved Security Vulnerabilities & Sole 4x Gold-Tier Record): In 2017-2018, I became the sole tester platform-wide to simultaneously hold Gold-Tier ratings across all four active testing practices (Security, Functional, Usability, and Localization) for over a year.
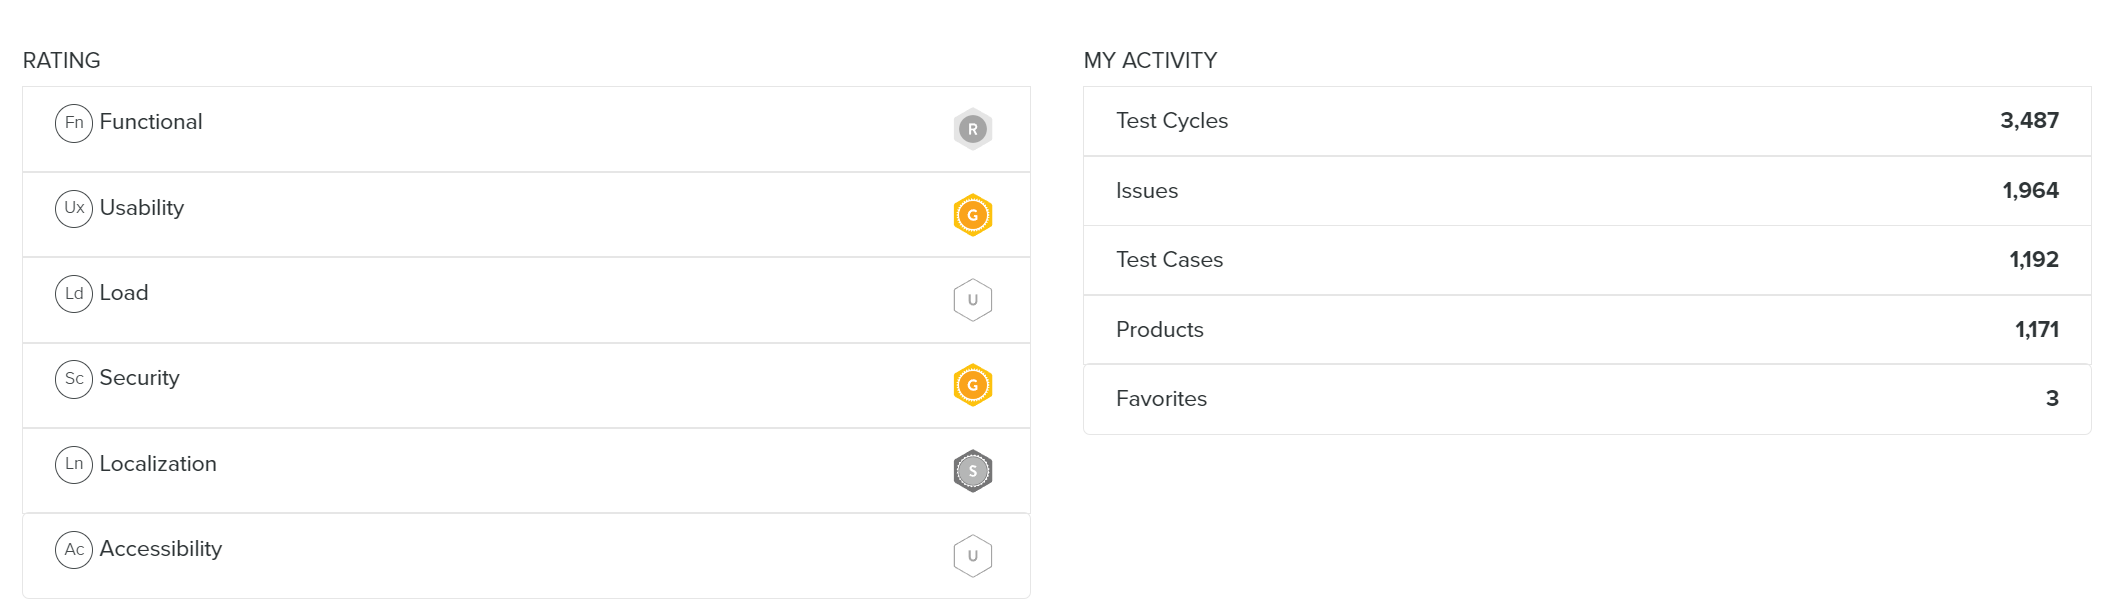
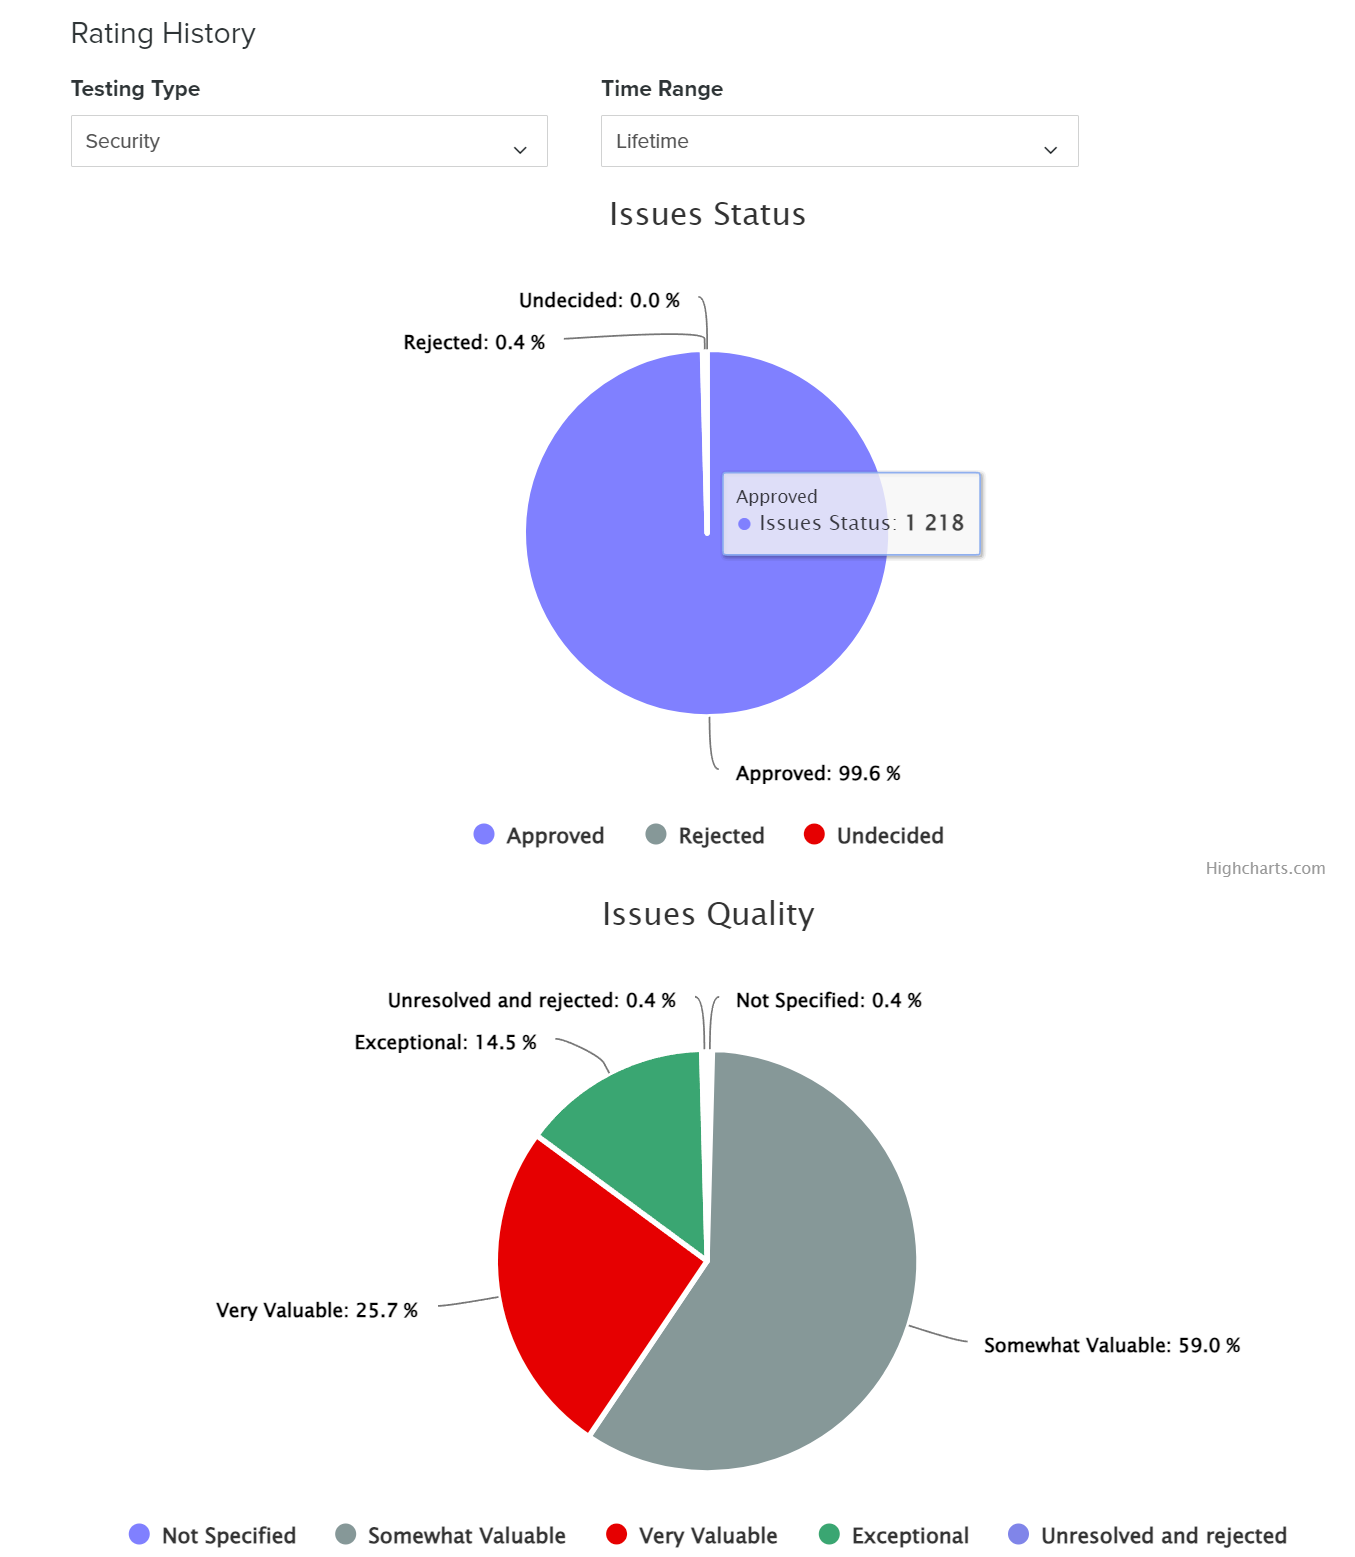
(Click images to verify: Official platform metrics [2026] showing Gold-Tier Security Rating, 4,050 total test cycles & 1,544 approved security issues at a 99.7% approval rate)
from
2025
TO
Present
(1+ Year)On-Device AI R&D
IMMER & IMMER Mobile: Offline Neural Memory & Agentic Engineering
The Project (Evolving into IMMER Mobile): I am expanding "IMMER" (Intelligent Multi-scale Memory via Emergent Resonance) into IMMER Mobile, an ultra-efficient, 100% offline mobile architecture designed to solve the static nature of LLMs. Unlike conventional RAG, IMMER implements Hebbian learning, Test-Time Neurogenesis, and Metabolic Aging/Crystallization so memory structures dynamically adapt and consolidate knowledge during interaction without catastrophic forgetting.
The Innovation: Efficient On-Device Plasticity:
Inspired by Google's Titans/MIRAS concepts and originally prototyped on desktop consumer GPUs (RTX 4080), IMMER Mobile brings dynamic memory states to local mobile and edge hardware by feeding lightweight "Soft Tokens" into a frozen core model rather than retraining heavy attention layers.
(Expanded research scope; paper scheduled for 2027)
The Engine: Agentic Training (MAKER): To train and validate this system reliably, I leverage the Cognizant Labs/UT Austin MAKER framework, decomposing workflows into micro-tasks with multi-agent voting and strict JSON schema validation to achieve near-zero error rates even on compact local models.
from
2018
TO
Present
(8+ Years)Education & Execution
Mastery Through Teaching, Certifications & Academic Studies
Full-Time IT & Security Lecturer (alfatraining GmbH, 06/2021-07/2022 & since 07/2026):
True mastery is proven when you can teach it. Since July 2026, I lead full-time, four-week intensive courses (160+ instruction hours per cohort) in Python Essentials (PCEP preparation), SQL Relational Databases, and AWS Cloud Administration & Management (CLF-C02 preparation).
Previously at alfatraining (06/2021-07/2022), I taught full-time, four-week CompTIA PenTest+ and ISTQB CTFL certification courses for IT administrators, managers, forensics specialists, and researchers (5-18 participants per cohort), covering Active Directory attacks, privilege escalation, DLL hijacking, pivoting, Nmap strategies, web/API exploitation, threat modeling, and compliance (BSI, NIST), building on intensive corporate Web Application Security bootcamps delivered in Manhattan/NYC (2018).
Verified Certifications & Academic Studies: Active credentials include Certified Entry-Level Python Programmer (PCEP, 07/2026), AWS Certified Cloud Practitioner (CLF-C02, 06/2026), PMI GenAI for Project Managers (03/2025), ISTQB CTFL (09/2021), CompTIA PenTest+ ce (07/2021), and ECDL Advanced Expert (2007), with CompTIA SecurityX and OffSec OSWE (WEB-200) currently in preparation. Alongside teaching, I am pursuing an English-language B.A. in Digital Business (AI Economics focus) at IU International University of Applied Sciences (since 08/2024, expected 2027), following my Abitur with a specialization in Physics and Mathematics (2021-2024).
Field-Grounded Pedagogy: Every module I teach is anchored in active offensive security and engineering practice, from securing banking cloud infrastructures and auditing enterprise APIs to reversing IoT protocols and dissecting DRM systems.
from
2008
TO
Present
(18 Years)Community Impact
Open Source & Community Leadership
Guest Mentor at University of Rostock (2021-2024): Invited by the Rostocker Hackspace, I regularly conducted voluntary workshops during the "Fachschaftswoche" for computer science students. Topics ranged from practical IT security to hands-on ethical hacking, bridging the gap between academic theory and industry reality.
Open Source Contributions (since 2008):
• Security Tooling: Active contributor to MobSF and ongoing collaboration with PortSwigger (Burp Suite bug reports and feature requests via their third-level support).
• Desktop & Browser Engineering: Created widely used Firefox extensions and contributed C++ code to Second Life Viewers (desktop client development and official JIRA bug triage from 2009-2013, with active C++ viewer development resumed in 2026).
Whether mentoring students or contributing code upstream, my goal remains the same: sharing practical engineering knowledge to build a more secure and open digital ecosystem.